For years, corporate leaders have faced a frustrating strategic paradox: their most valuable asset is proprietary data, yet privacy laws, competitive secrecy, and cyber risks keep that data locked in isolated silos.
Now, a breakthrough highlighted in the Top 10 Emerging Technologies of 2026, a report by the World Economic Forum in collaboration with Frontiers, the open-science publisher, is turning that roadblock into a competitive advantage. Called lattice-based cryptography, the next-generation security technology underlying both fully homomorphic encryption and the post-quantum cryptography standards issued by the U.S. National Institute of Standards and Technology (NIST), it is best known for shielding corporate secrets from future quantum computers. For business leaders, however, another potential payoff is something entirely different: it opens the door to more advanced applications down the road, such as the ability to pool sensitive data with partners and train powerful AI models without ever exposing a single underlying record.
The math is standardized and ready. Corporate execution is not. According to the 2026 Quantum Readiness Outlook from DigiCert, a global issuer of security certificates, while 87% of organizations say they are planning or testing post-quantum cryptography initiatives, only 7% have actually deployed quantum-safe or hybrid encryption across most of their digital certificates—barely budging from the year before.
When organizations do push past the planning phase, the commercial potential is striking. Consider what happened at Asan Medical Center, the teaching hospital of the University of Ulsan College of Medicine, located in Seoul, South Korea. Researchers used a lattice-based technique called fully homomorphic encryption to train AI models across more than 300,000 patient records from three separate hospitals, according to the report. Not a single hospital’s raw data ever left its own servers, yet the resulting AI outperformed anything one institution could have built alone.
Computing on encrypted data is slower than working with raw data. Yet for executives accustomed to multiyear legal gridlock, that computational drag is a bargain. Daniele Micciancio, a computer science professor at the University of California, San Diego, who helped pioneer the field and co-authored the lattice cryptography section of the report, recalls a health agency official putting the trade-off bluntly at a recent cryptography meeting: “The speed that you have now is already much faster than the alternative of putting a bunch of lawyers from different hospitals in a room and getting them to agree on how they could share the data.”
For executives deciding where to place their AI bets today, practitioners urge a clear-eyed view of what cryptography can—and cannot—solve on its own. A. Aldo Faisal, professor of AI and neuroscience at Imperial College London and chair in digital health at the University of Bayreuth, is lead investigator for Nightingale AI, a large-scale European multimodal foundation model for health. He notes that while homomorphic encryption works well for pooled statistics and smaller predictive models, it remains far too computationally expensive for training massive foundation models.
Instead, large-scale initiatives like Nightingale AI rely primarily on federated learning and trusted research environments, where data stays local and algorithms travel to the data. In those projects, Faisal says, the real binding constraints are not cryptographic—they are “governance, interoperability, and data quality.”
“Post-quantum cryptography is the lock on the door,” Faisal says, “but we have to agree on who gets the keys and how.”
Hiding Secrets In A Mathematical Fog
To understand why global institutions are suddenly rallying behind lattice cryptography, it helps to see why today’s digital locks are at risk. Most current encryption relies on math problems—such as factoring massive numbers—that take conventional computers centuries to solve. In the mid-1990s, mathematician Peter Shor proved that a sufficiently powerful quantum computer could crack those problems in minutes.
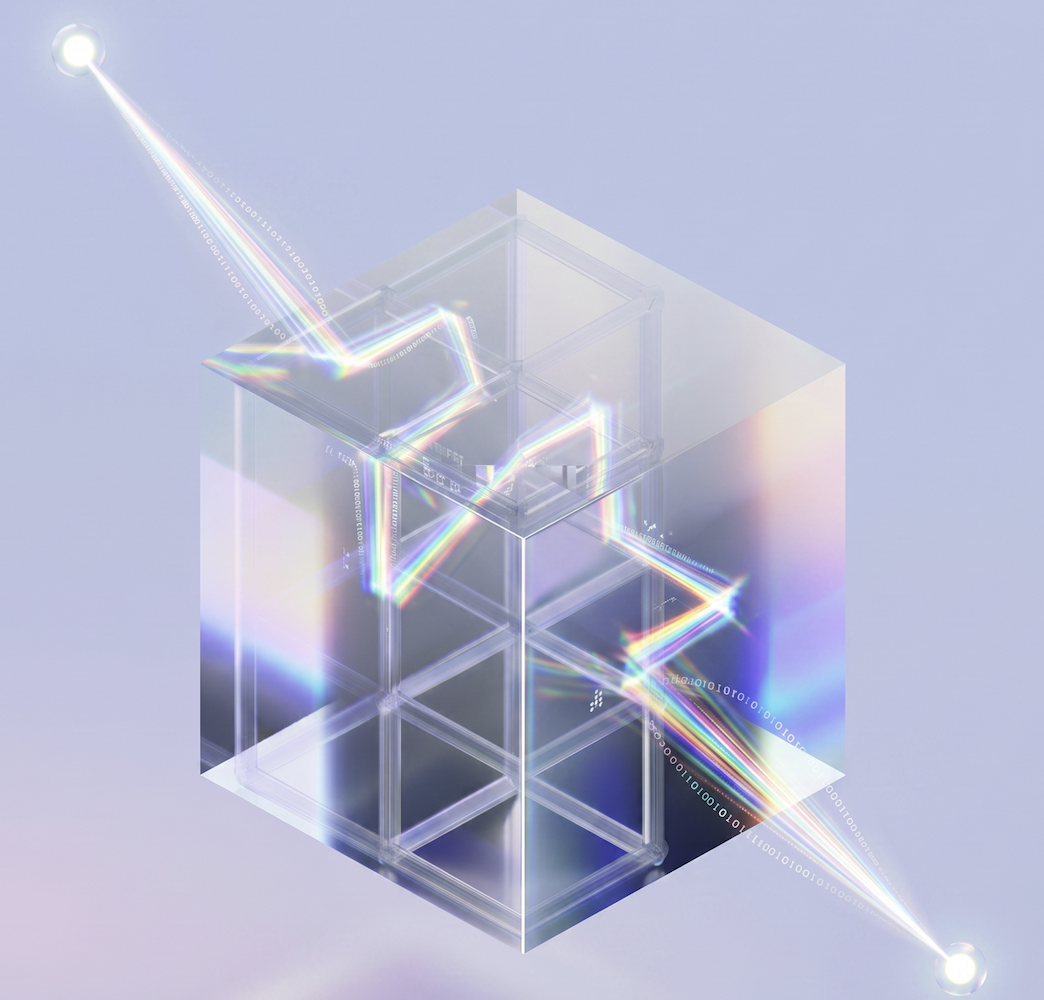
Lattice cryptography does not simply build a stronger lock. Instead, it hides data inside a vast, multidimensional grid of mathematical points—like choosing one specific intersection inside a sprawling city with hundreds or even thousands of dimensions. During encryption, the system deliberately introduces tiny, random errors, filling that city with thick fog. From the outside, an attacker sees millions of plausible intersections that look nearly identical to the real one. Even a quantum machine cannot see through the fog to pinpoint the true location.
Micciancio is refreshingly candid about what that guarantees. “We don’t know for sure [that it is unbreakable],” he says. “I think it is important to be honest about that. But at the same time, it is still our best bet.” Unlike older systems where hackers repeatedly uncovered “weak keys” through trial and error, mathematicians proved three decades ago that randomly chosen lattice keys are reliably hard to crack almost every single time. Lattice-based schemes have withstood 30 years of scrutiny from both classical and quantum codebreakers.
Because the data is protected by this mathematical fog rather than locked inside an impenetrable box, computers can perform calculations through the fog without ever lifting the veil. Meanwhile, recent lattice protocols have slashed execution time from 90 seconds to 20 milliseconds. That leap allows companies to verify regulatory rules—such as patient consent or cross-border data residency—automatically at the exact moment data moves, rather than relying on costly, after-the-fact compliance audits.
Why the Quantum Clock Just Sped Up
For two decades, whenever experts were asked when a code-breaking quantum computer would arrive, the answer was always the same: 10 years away. That cushion has vanished.
“Companies are starting to shrink this deadline,” Micciancio notes, pointing out that tech giants like Google are building quantum hardware themselves and know firsthand how quickly error-correction breakthroughs are advancing. Google has committed to completing its own post-quantum transition by 2029. Governments and financial networks are moving on similar schedules: the European Union designated 2026 as the starting year for public-sector migration, the U.S. National Security Agency mandates quantum-safe algorithms for new national security systems by January 2027, and the global banking network SWIFT is actively planning its transition.
For CEOs, the danger is not a distant sci-fi apocalypse; it is happening today. Adversaries are already executing “harvest-now, decrypt-later” attacks—intercepting and stockpiling encrypted corporate secrets, financial records, and intellectual property off the open internet, waiting for quantum machines to unlock them later. Waiting until quantum computers make headlines will be too late.
That urgency is sharpest in industries like healthcare and life sciences, where secrets do not expire. Unlike a credit card number that can be canceled, a patient’s genomic and medical history remains sensitive for an entire lifetime—spanning decades from the era of paper and punch cards to modern cloud databases. As Faisal puts it, organizations must protect those records today “against computers that don’t exist yet,” especially if quantum computing experiences its own sudden “ChatGPT moment”—exploding in capability and collapsing in price just as satellite launches and electric-vehicle batteries did before it.
Still, industry surveys reveal a glaring blind spot between boardroom rhetoric and execution. Fewer than half of organizations—just 44%, according to DigiCert—have built a formal transition plan or inventoried their encryption. A separate 2026 study of more than 4,100 IT and security practitioners globally, conducted by the Ponemon Institute, an independent cybersecurity research firm, and Entrust, found that only 43% have full visibility into where their encryption keys and certificates even live, making asset discovery their single biggest migration concern. As Micciancio observes: “If companies were to invest in this transition as much as they are investing in AI, we would already have post-quantum cryptography everywhere.”
Three Traps For Business Leaders
Even for companies ready to act, upgrading to lattice cryptography is not a simple software patch. As organizations begin migrating, executives must navigate three operational traps:
- The Small-Device Bottleneck: Lattice cryptography demands more computing power than legacy encryption. While cloud servers and smartphones handle it easily, billions of tiny industrial sensors, medical wearables, and legacy factory machines cannot. The fix, Micciancio explains, is architectural: small factory sensors do not need to run heavy lattice math themselves. Instead, they can use fast, lightweight “symmetric” encryption—which is already largely resistant to quantum attacks—to talk to a central factory computer that handles the heavy post-quantum lifting.
- The Human Engineering Cost:The biggest expense is not buying new algorithms; it is rewriting corporate software without introducing sloppy deployment bugs. As the math becomes harder to break, hackers are targeting physical and software flaws—such as “timing attacks,” where attackers deduce secret keys by measuring how many milliseconds a chip takes to process data. “Cryptography is often used as some kind of magic wand,” Micciancio warns. “People say, ‘Oh, the application is secure because we are using encryption.’ If you are not using it the right way, the application is not going to be secure.”
- The “Zero-Wiggle-Room” Compliance Rule:Encoding compliance rules directly into automated cryptographic checks eliminates human bottlenecks, but it also removes human discretion. As Faisal notes, realizing a seamless cross-border data future—such as the European Health Data Space envisioned for 2031—depends heavily on interoperability standards, consent infrastructure, and legal harmonization. If a company or regulator writes vague or flawed privacy policies into its code, the software will enforce those mistakes rigidly and instantaneously at scale.
The good news is that executives needn’t worry that incompatible global standards will fracture cross-border business like mismatched travel power plugs. Digital systems can automatically negotiate which encryption scheme to use, and leading organizations are already deploying “hybrid” encryption—wrapping data in both traditional and lattice-based locks simultaneously so systems remain protected whether quantum computers arrive tomorrow or decades from now.
What Leaders Should Do Next
In many ways, the transition is already quietly underway. Major web browsers, cloud providers, and secure messaging platforms have begun rolling out lattice-based protections behind the scenes faster than even researchers anticipated, says Micciancio.
Yet in cybersecurity, attackers do not target your strongest defenses; they target the blind spots security teams cannot yet see—and, according to the Ponemon study, 57% of organizations lack full visibility into where their encryption keys and certificates live. As Micciancio sees it, completing the shift over the next five years faces “no fundamental obstacle.” Whether a company emerges more secure—and potentially better positioned in the long run to turn locked-up data into collaborative AI value—comes down to two familiar boardroom variables, he says: “cost and focus.”
This article is content that would normally only be available to subscribers. Become a subscriber to see what you have been missing